Software
Implementing Passwordless Authentication (5-Step Plan)
Implementing passwordless authentication with phishing-resistant passkeys: how login works, Microsoft Entra steps, recovery, and a 5-step rollout plan.
Implementing passwordless authentication means replacing passwords with phishing-resistant credentials, usually passkeys, FIDO2 security keys, or device biometrics, and rolling them out in phases so every user has a working sign-in method and a safe recovery path before the password is switched off.
The hard part is rarely the technology. It is the order of operations: who goes first, what happens when a device is lost, which fallback stays available, and how the project is budgeted so it does not stall after the pilot.
Quick answer
To implement passwordless authentication, inventory every login point, pick a primary phishing-resistant authentication method (passkeys for most staff, hardware security keys for admins), set up a recovery flow, pilot with one team, then expand in waves. Remove passwords only after adoption is confirmed, not on a fixed date.
Key takeaways
- Not every passwordless method is phishing-resistant: magic links and one-time codes can still be phished; passkeys and FIDO2 keys cannot be replayed on a fake site.
- Recovery is the real security boundary. A strong login with a weak password reset flow just moves the attack.
- The weakest fallback a user can still choose sets your real security level, so rank and retire fallbacks deliberately.
- Use passkeys on devices people already carry for most staff, and reserve hardware keys for privileged accounts to avoid buying keys nobody uses.
- Microsoft reported a 98% sign-in success rate for passkeys versus 32% for passwords, so the user experience case is as strong as the security case.
What Is Passwordless Authentication and Why Implement It Now?
Passwordless authentication is any authentication method that lets a person prove their identity without a password. Instead of a shared secret typed into a box, the user proves something they have, like a phone or security key, and usually something the user is (a fingerprint or face) or knows (a device PIN).
Passwords have fallen out of favor for a simple reason: a password is a secret stored in two places, the user's memory and the server's database. Both leak. People reuse the same password across multiple sites, which makes credential stuffing cheap, and any breach of one service puts accounts elsewhere at risk.
The shift has moved from theory to defaults. In May 2025, Microsoft announced that new Microsoft accounts would be passwordless by default, and Apple, Google, and Microsoft all sync passkeys across a user's devices and accounts. For most companies, the question is no longer whether to go passwordless but how to do it without locking people out.
Treat the project as a business decision, not only a security upgrade. It touches budget, support staffing, and vendor contracts, which is why it sits naturally among other core business concepts that finance and operations teams need to share a vocabulary on.
Passwordless MFA versus password-based authentication
Password-based authentication checks one thing: whether you know a string. Adding a code makes it multifactor authentication, but the password is still there to steal. Passwordless MFA combines two factors without the password: the device holding the key, plus a biometric or PIN that unlocks it.
That distinction matters when you write policy. Each authentication factor should be something an attacker cannot collect from a phishing page or a leaked database. A device-bound private key unlocked by a fingerprint meets that bar. A password plus an SMS code does not.
How Does Passwordless Authentication Work?
Most modern passwordless authentication systems run on FIDO2, a set of open standards made of the W3C WebAuthn browser API and the FIDO Alliance's CTAP protocol. Understanding the basic authentication flow explains why it resists phishing in a way passwords never can.

The cryptographic key pair behind every passkey
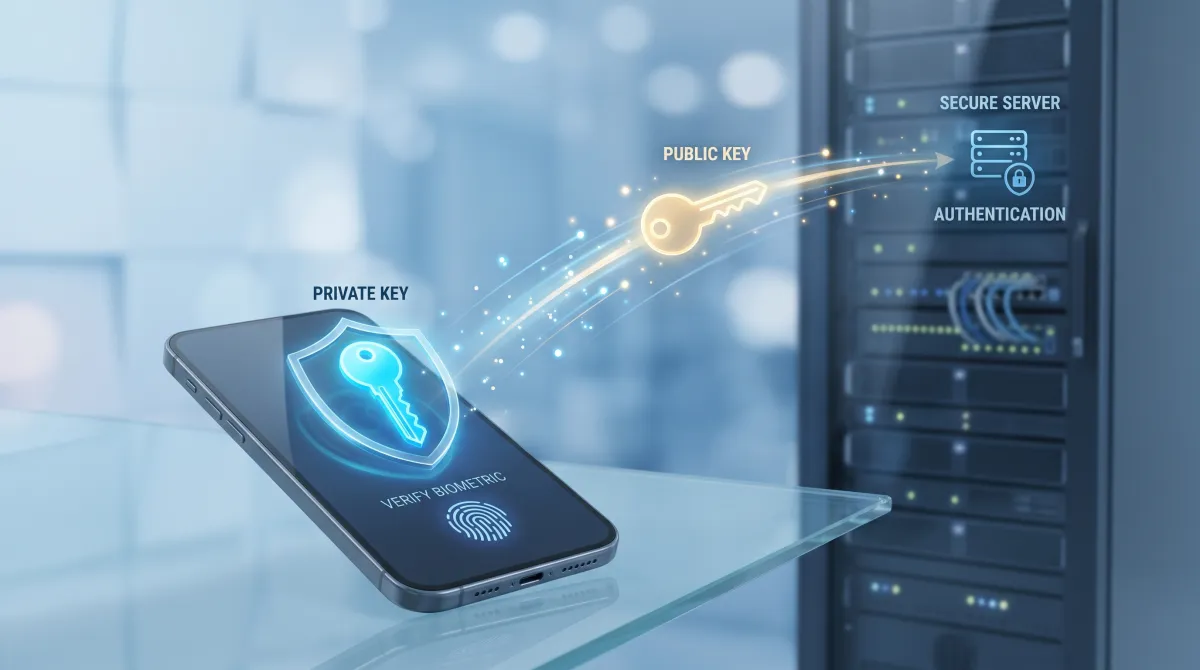
When a user registers, their device creates a unique cryptographic key pair for that one website or app. The public key goes to the server. The private key stays on the device, protected by the secure hardware chip, and the biometric data never leaves the device either.
At login, the server sends a random challenge. The device asks the user to verify with a fingerprint, face scan, or PIN, then signs the challenge with the private key. The server checks the signature against the stored public key. No secret crosses the network, so there is nothing for an attacker to steal or replay.
Notice what the server never does: it never asks the user to authenticate by sending a secret. Verification happens in two separate places. The device performs local user verification, and the server performs cryptographic verification of the signature. Neither side ever sees a secret it could leak.
Why this is phishing-resistant
Each credential is bound to the domain where it was created. If a phishing page at a look-alike address asks for a sign-in, the browser will not offer the real site's passkey, because the domains do not match. The user cannot be tricked into handing it over, even on a convincing fake page.
That is the key distinction between phishing-resistant authentication and older multifactor authentication. A one-time code from SMS or an authenticator app can be typed into a fake site and relayed in real time. A FIDO credential cannot be phished that way, because the browser enforces the domain check, not the human.
Where tokens fit in
After the device signs the challenge, the identity provider issues a session token to the app. That token is what keeps the user signed in. Passwordless login protects the front door, so you still need sensible token lifetimes and device checks to protect the session afterward.
Common Passwordless Authentication Methods Compared
There are different authentication methods available, and they are not equally strong. The table below compares the common passwordless authentication options most organizations consider, ranked by how well they hold up against phishing. Use it to decide which authentication method becomes the default for each group.
| Method | Phishing-resistant? | Best for | Main weakness |
|---|---|---|---|
| Synced passkeys | Yes | General staff and customers | Security depends on the cloud account that syncs them |
| Device-bound passkeys (e.g. in Microsoft Authenticator) | Yes | Staff in regulated or managed environments | Lost device means re-registration |
| FIDO2 security keys | Yes | Admins and privileged accounts | Hardware cost, users forget or lose keys |
| Windows Hello for Business / platform biometrics | Yes | Employees on managed laptops | Tied to one device |
| Authenticator app push or codes | No (codes can be relayed) | Transitional MFA | Push fatigue, real-time phishing |
| Magic links and email or SMS OTPs | No | Low-risk consumer sign-ups | Email or phone takeover, SIM swap |
Passkeys
Passkeys are passwordless credentials that users can use with their phone, laptop, or tablet, unlocked by the same biometric or PIN they already use to log in to the device. Synced passkeys are backed up through iCloud Keychain, Google Password Manager, or a third-party password manager, which makes them easier for users to recover.
Security keys and FIDO2 hardware
Physical security keys plug in over USB or tap over NFC. They hold the private key in dedicated hardware and are the strongest common option for administrators, finance approvers, and anyone whose account would be a high-value target.
Biometric authentication
Biometric authentication uses unique physical characteristics such as a fingerprint or facial recognition. In a FIDO setup, biometrics do not authenticate the user to the server directly. They unlock the private key locally, so the fingerprint template stays on the device and is never sent to the service.
That design answers the most common staff objection. When you use biometrics this way, the company never holds a database of employee faces or fingerprints. Facial recognition happens on the mobile device or laptop, and only a signed result reaches the server.
Authenticator apps, magic links, and one-time codes
Authenticator apps such as Microsoft Authenticator can do push approvals, one-time codes, and, in newer versions, store device-bound passkeys. Push and codes are better than a password alone, but they are not phishing-resistant passwordless methods.
A magic link is a one-time sign-in URL sent by email. Magic links and OTPs sent by email or phone are convenient, yet they only move trust to the inbox or the phone number. If an attacker controls the inbox, the magic link works for them too.
Which Authentication Method Fits Each User Group?
The right authentication method depends on what an account can do, not on job title. A practical rule: the more damage a stolen login could cause, the less you should rely on methods like push approvals or email codes, and the more you should rely on hardware-bound keys.
| User group | Primary method | Backup credential | Fallback to block |
|---|---|---|---|
| Global and IT admins | FIDO2 security key | Second security key stored securely | Password, SMS, push approval |
| Finance and payment approvers | FIDO2 key or device-bound passkey | Second registered device | Password, SMS |
| General office staff | Synced or device-bound passkey | Passkey on a second device | Password after enrollment |
| Frontline and shared devices | Security key or badge-based sign-in | Spare key held by the shift lead | Shared passwords |
| Customers | Synced passkey | Email code for low-risk accounts | Password once passkey share is high |
The "fallback to block" column is the one most rollouts skip. A user’s strongest credential protects nothing if the sign-in page still offers a weaker option, so every row needs an end date for its weakest method.
Should One User Register Different Methods?
Yes, and most users should. Registering different methods on separate devices is what makes a passwordless setup survivable: if one credential is lost, another still works. The rule is that every authentication method a user holds should be phishing-resistant, or at least ranked and scheduled for removal.
A sensible pattern for office staff is a passkey on the phone plus Windows Hello or Touch ID on the laptop. Both rely on the device unlocking a private key with a fingerprint, facial recognition, or PIN, so neither adds a weaker path. Administrators add a second hardware key kept somewhere safe.
Where it goes wrong is mixing strengths. If the same account accepts a passkey and an SMS code, the account is only as strong as the SMS code. Policy should allow each authentication method only for the groups that need it, and log every time a weaker one is used.
What Are the Benefits of Passwordless Authentication?
The key benefits of passwordless authentication fall into four groups: security, user experience, support cost, and compliance. It helps to understand the benefits in that order, because security is what gets the project approved and user experience is what drives authentication adoption.
Security: eliminate the credential most attacks start with
Going passwordless helps eliminate the credential that phishing, credential stuffing, and password spraying depend on. There is no password to reuse, guess, or leak in a breach. Google told KrebsOnSecurity in July 2018 it had no reported or confirmed account takeovers among its more than 85,000 employees since requiring physical security keys in early 2017.
User experience: faster and more reliable sign-in
A good passwordless login is a fingerprint or face scan, not a typed string plus a code. Microsoft's May 2025 passkey announcement reported a 98% sign-in success rate for passkeys compared with 32% for passwords. Fewer failed logins means less friction for every employee and customer, and a method that is both secure and user-friendly is one people stop trying to bypass.
Support cost: fewer password reset tickets
Forgotten and expired passwords are a steady source of help desk tickets. Removing the password removes most of that queue, although some volume shifts to device registration and recovery. Measure ticket categories before and after the pilot so the savings claim rests on your own data, not a vendor estimate.
Compliance requirements
Phishing-resistant MFA increasingly shows up in public-sector rules. OMB memo M-22-09, issued in January 2022, directed US federal agencies to require phishing-resistant MFA for their staff by the end of fiscal year 2024.
Private companies are generally not bound by that memo, but similar questions can appear in customer security reviews and cyber insurance applications, especially about privileged accounts. A passwordless rollout is one of the cleanest ways to meet compliance requirements of that kind.
Remote work without a VPN password
Remote work made the password the weakest link in many companies, because staff log in from home networks and personal devices. A passkey bound to a managed laptop lets people verify their identity using hardware the company controls, wherever they sit, without one more password to phish.
A passwordless login is only as strong as the way you recover it. Fix recovery first, then remove the password.
How to Implement Passwordless Authentication in 5 Steps
The safest way to implement passwordless authentication is a staged rollout that keeps a fallback in place until each group has proven it can sign in without help. These five steps work for most mid-sized organizations; adjust the wave sizes to your headcount.
Step 1: Inventory every login point
List every app, VPN, admin console, and legacy system that still uses password authentication. Note which ones support FIDO2 or WebAuthn natively, which can sit behind a single sign-on identity provider, and which only accept a password. The legacy list decides your timeline more than anything else.
Step 2: Choose a primary method per user group
Match the method to the risk. A reasonable starting split is passkeys for general staff, FIDO2 security keys for administrators and finance approvers, and platform biometrics such as Windows Hello for Business on managed laptops. Consider using authenticator apps only as a transitional step, not the end state.
When choosing a passwordless authentication solution, consider the following questions. Does it support passkeys and security keys natively? Can policy block a weaker authentication method per group? Does it log which method each user actually used to log in? A vendor that cannot answer all three will slow the later waves.
Step 3: Design onboarding and recovery before launch
Decide how a new hire gets their first credential and how someone who loses a phone gets back in. Identity platforms offer time-limited bootstrap codes for this, such as Microsoft Entra's Temporary Access Pass. Require at least two registered credentials per person, for example a phone passkey plus a laptop passkey or a backup security key.

Do not let recovery fall back to an email link or a help desk agent reading out a reset code. That turns the recovery flow into the easiest way for an attacker to bypass the phishing-resistant login you just paid for.
Recovery should require staff to verify identity at least as strongly as the original enrollment, for example a video call with photo ID or approval from the person's manager before any bootstrap code is issued.
| Credential type | If the device is lost | Recovery check to require |
|---|---|---|
| Synced passkey | Sign in on a new device through the Apple, Google, or password manager account | Protect that sync account with its own phishing-resistant sign-in |
| Device-bound passkey | Use a second registered credential, then re-register | Manager approval or in-person ID check before a bootstrap code |
| FIDO2 security key | Use the backup key, then revoke the lost one | Revoke immediately in the identity console |
| Platform biometrics on a laptop | Re-enroll on the replacement laptop | Temporary Access Pass issued after verification |
Step 4: Pilot, measure, and expand in waves
Start with IT and one willing department. Track enrollment rate, failed sign-ins, and help desk tickets by category for at least a few weeks. Expand only when tickets stabilize, then roll out in waves by team, office, or device readiness rather than by calendar date.
Communicate the change as a benefit, not a mandate. Tell staff exactly what they will see at login, how long registration takes, and who to call. Authentication adoption rises fastest when the first wave reports that sign-in got easier.
Step 5: Enforce, then remove the password
Once a group is enrolled, enforce the phishing-resistant method through policy and block weaker fallbacks for that group. Removing or randomizing the password comes last, and only then can you eliminate it from the account entirely. Leaving passwords active "just in case" keeps the old attack surface open indefinitely.
Every rollout of this kind is a trade-off between faster, safer logins and new dependencies on vendors and devices. Weighing it with the same lens you would apply to the benefits and risks of innovation keeps the decision honest about both sides.
How long does each phase usually take?
Timelines depend mostly on legacy systems and device readiness, not on the identity platform. The ranges below are planning assumptions for a mid-sized company, not benchmarks; replace them with your own pilot data.
| Phase | Planning range | Exit signal |
|---|---|---|
| Inventory and method choice | 2-4 weeks | Every login point mapped to a method |
| Pilot (IT plus one team) | 3-6 weeks | Tickets stable, enrollment above target |
| Rollout waves | Several months | Each wave enforced before the next starts |
| Password removal | Per wave | No password sign-ins logged for the group |
How to Measure Passwordless Authentication Adoption
Enrollment numbers alone are misleading. A user can register a passkey and still sign in with a password every day. The useful question is which authentication method people actually use to authenticate, and how often the weaker options still get chosen.
| Metric | What it tells you | When to act |
|---|---|---|
| Share of sign-ins by method | Real usage, not just registration | Password share is not falling wave over wave |
| Users with two or more credentials | Recovery readiness | Any privileged user has only one |
| Failed sign-ins per user | Friction in the new flow | A spike after a wave goes live |
| Recovery requests per week | Load on the help desk and the recovery path | Volume stays high after the first month |
| Fallback sign-ins by enrolled users | Whether weak methods are still the easy path | Any fallback use by admins |
Most identity platforms expose sign-in logs that record the authentication method used for each attempt. Export them weekly during the rollout to verify progress, and review them with the group that approved the budget, so success is judged on behavior rather than on the number of keys shipped.
Break the numbers down by authentication method and by user group. A single company-wide percentage hides the one department where the password is still the default authentication method.
How to Budget a Passwordless Rollout Without Wasting Hardware
This is where most guides stop and where many projects stall: the budget conversation after the pilot. Framing costs in the terms finance already uses makes approval faster and keeps the rollout funded through the later waves.
Security keys as depreciating assets
Depreciation meaning, in plain terms, is spreading the cost of an asset over its useful life instead of expensing it all at once. Whether a batch of security keys is capitalized or expensed depends on your company's capitalization threshold, so ask finance which applies before you quote a year-one cost. The depreciation definition they use changes how the project looks on paper.
Avoiding overproduction of security keys
A common mistake in hardware programs is a form of overproduction: buying keys for every employee up front, then finding many sitting in drawers after staff turnover or reorganizations. Passkeys on phones and laptops people already carry avoid most of that waste. Buy hardware keys for privileged accounts and a small spare pool, not the whole workforce.
Economies of scale on the identity platform
The economies of scale definition applies directly: your fixed costs for the identity platform, configuration, and training are spread across more users as the rollout grows. The cost of onboarding the 500th employee is far lower than the 5th, which is why phasing helps cash flow without undermining the long-term case.
Choosing a managed identity provider also adds a new intermediary between your company and its sign-in data, a form of reintermediation worth weighing before you sign a multi-year contract. Check export options and what happens to registered credentials if you switch vendors.
| Cost item | Typical accounting treatment | How to control it |
|---|---|---|
| Identity platform licenses | Operating expense (subscription) | Phase seats with each rollout wave |
| Hardware security keys | Expensed or capitalized, per your threshold | Buy for privileged users plus a spare pool |
| Implementation and training | Usually operating expense | Reuse pilot materials for later waves |
| Help desk time | Existing staff cost | Track reset tickets before and after |
Skip the finance conversation and the rollout usually stalls right after the pilot, when budget owners start asking hard questions. IT leads pushed into that position often recognize the pattern described in signs you are being set up to fail at work: responsibility for the outcome without authority over the budget.
Phishing-Resistant Passwordless in Microsoft Entra ID
Many organizations run their workforce identity on Microsoft Entra ID, so it is worth knowing how the pieces map. Entra supports several phishing-resistant passwordless options: passkeys (FIDO2) including device-bound passkeys in Microsoft Authenticator, Windows Hello for Business, FIDO2 security keys, and certificate-based authentication.
Conditional Access includes built-in authentication strengths, one of which requires phishing-resistant MFA. A practical pattern is to apply that strength first to admin roles, then to sensitive apps, then to everyone. Temporary Access Pass handles first-time registration so new users never need a password at all.
The same sequence applies when you deploy passwordless on other identity platforms such as Okta or Google Workspace: register strong credentials, enforce them with policy for one group at a time, and only then turn off the weaker methods. That order lets you roll out passwordless authentication across workforce and admin accounts without a single cutover day.
Passwordless Authentication for Customer Login
Customer-facing sign-in follows the same principles with one difference: you cannot issue hardware or force enrollment. Offer passkeys at sign-up and after a successful login, and keep the existing authentication method available until the customer opts in.
For consumer apps, the realistic goal is to adopt phishing-resistant credentials as the default path while a magic link or email code remains a fallback for low-risk accounts. Track the share of customers who authenticate with passkeys, and tighten the fallback once that share is high enough to absorb the change.
When Does a Passwordless Rollout Fail?
Passwordless projects rarely fail on cryptography. They fail on edges the plan did not cover. Watch for these four in particular.
- Weak recovery. A phishing-resistant login paired with an email-based reset is only as strong as the inbox.
- Shared and frontline devices. Kiosks, warehouse scanners, and shared workstations need a different approach, often security keys or badge-based sign-in.
- Legacy apps. Systems that only accept a password keep a password alive somewhere unless they move behind single sign-on.
- Mixing methods without ranking them. If users can always fall back to SMS codes, attackers will choose that path.
For example, imagine a company that enrolls 90% of staff in passkeys but keeps SMS codes as an always-available fallback. An attacker running a phishing kit simply selects the SMS option. Until the fallback is removed for enrolled users, the organization has added convenience but not much security.
The fix is a ranked list. Write down every authentication method still enabled, order them from strongest to weakest, and treat the bottom of the list as your real security level. Then remove methods from the bottom up, one user group at a time.
Passwordless Authentication: Frequently Asked Questions
How does passwordless authentication work?
Passwordless authentication works by having the user's device sign a login challenge with a private key that never leaves the device. The user unlocks that key with a fingerprint, face scan, or PIN, and the server verifies the signature with the matching public key.
Is passwordless authentication more secure than passwords plus MFA?
Yes, when it uses phishing-resistant methods such as passkeys or FIDO2 security keys. Traditional MFA codes can be relayed by a phishing site in real time, while FIDO credentials are bound to the real domain and will not work on a fake one.
What are the most common passwordless authentication methods?
The most common passwordless authentication methods are passkeys, FIDO2 security keys, platform biometrics such as Windows Hello, authenticator app push approvals, and magic links or one-time codes. Only the first three are phishing-resistant.
Are magic links passwordless authentication?
Magic links are passwordless, but they are not phishing-resistant. They shift security to the email account, so they suit low-risk consumer sign-ups better than workforce or admin access.
Does passwordless authentication store employees' biometric data?
No, not in a FIDO2 or passkey setup. The fingerprint or face template stays on the user's device and only unlocks the private key, so the server receives a signed challenge, never the biometric itself.
How long does it take to implement passwordless authentication?
For a mid-sized company, plan on several months from inventory to password removal, because rollout waves and legacy apps set the pace. The pilot itself usually fits in a few weeks; treat any timeline as a planning assumption until your own pilot data confirms it.
Do we still need passwords for anything after going passwordless?
Sometimes, for legacy apps that cannot use single sign-on or modern authentication. Keep those on a short, tracked list with a retirement plan, and protect them with a strong unique password managed by a password manager in the meantime.